
Updated: November 11, 2026 | Category: Cybersecurity | Vendor: Microsoft
Quick Answer: What Is CVE-2026-124194?
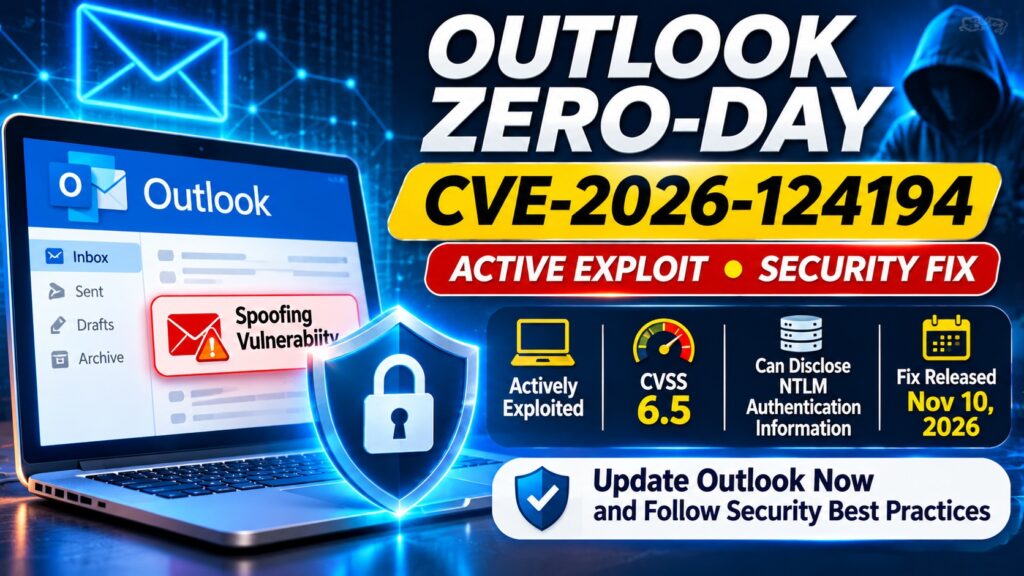
CVE-2026-124194 is an actively exploited Microsoft Outlook spoofing vulnerability patched on November 10, 2026. An attacker can create a malicious message file that, when opened in an affected Outlook desktop application, may cause Windows to send NTLM authentication information to an attacker-controlled network location without the usual external-content warning.
Microsoft rates the flaw Moderate (CVSS 6.5), but confirmed exploitation makes it a high-priority security update.
What to do now: Install the latest applicable Microsoft 365 or Office security update, avoid opening unexpected Outlook message files, and ask your IT administrator to investigate any suspected exposure.
Microsoft Outlook Zero-Day: Latest November 2026 Update
Microsoft released its November 2026 Patch Tuesday security updates on November 10, addressing vulnerabilities across Windows, Microsoft 365, Office and other supported products.
One of the most urgent issues is CVE-2026-124194, a spoofing vulnerability affecting certain versions of Microsoft Outlook.
The issue attracted particular attention because attackers were already exploiting it before the security fix became available.
Microsoft’s advisory classifies the vulnerability as Moderate, rather than Critical. However, a vulnerability’s severity score does not tell the entire story. A flaw that is actively being used against real users may deserve more immediate attention than a theoretically severe issue for which no exploitation has been observed.
The US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-124194 to its Known Exploited Vulnerabilities catalog on November 10, 2026.
That listing provides additional evidence that organisations should prioritise the available fix.
Also Read : Microsoft November 2026 Patch Tuesday
CVE-2026-124194 Vulnerability Details
| Security Detail | Confirmed Information |
|---|---|
| CVE identifier | CVE-2026-124194 |
| Product | Microsoft Outlook |
| Vulnerability category | Spoofing / unsafe action without appropriate UI warning |
| CWE classification | CWE-356 |
| CVSS v3.1 | 6.5 — Medium |
| Microsoft severity | Moderate |
| Attack vector | Network |
| User interaction | Required |
| Known exploitation | Yes |
| Patch publication | November 10, 2026 |
| CISA KEV listing | Added November 10, 2026 |
| Primary impact | Potential disclosure of authentication information |
These details are based on Microsoft’s published vulnerability record and the corresponding CISA information.
How Does the Outlook Zero-Day Work?
Microsoft Outlook is widely used to manage business email, calendars, contacts and messages.
Like other desktop applications, it may interact with files, links and resources referenced by content that users open.
CVE-2026-124194 involves Outlook failing to provide an appropriate warning before an unsafe action.
The attack can unfold as follows:
- An attacker prepares a specially crafted Outlook message file.
- The attacker delivers the file to a potential victim, such as through a phishing email.
- The recipient opens the malicious file using a vulnerable Outlook application.
- Outlook may attempt to access an attacker-controlled network location without displaying the expected external-content warning.
- Windows authentication behaviour may expose NTLM authentication information to the remote system.
- The attacker may attempt to misuse that information for credential attacks or impersonation.
The attack requires user interaction and network connectivity. It is not accurate to claim that every ordinary email automatically triggers this vulnerability simply by appearing in the inbox.
It is also important to distinguish credential disclosure from confirmed account takeover. Exposing authentication material creates a security risk, but does not prove that an attacker successfully accessed the user’s account.
What Is an NTLM Hash, and Why Does It Matter?
NTLM is a Windows authentication technology used in some environments for network access.
When Windows authenticates to certain network services, it can exchange authentication information derived from a user’s credentials.
Under the wrong conditions, an attacker may capture an NTLMv2 challenge-response value during an authentication attempt.
Attackers may then try to crack the captured material offline or abuse it in authentication-related attacks where environmental conditions permit.
This is different from Outlook simply displaying the user’s password on the screen. The vulnerability concerns authentication data transmitted during a network interaction.
Why Businesses Face Particular Risk
Corporate Windows environments may use shared network resources, directory services and legacy authentication protocols.
If an attacker obtains useful authentication information, the potential consequences may extend beyond the original email message.
Depending on the account’s permissions and the organisation’s security controls, attackers might attempt to access internal resources or impersonate an employee.
For this reason, IT teams should assess the exposure of affected endpoints and review whether NTLM authentication is still required in their environment.
Which Microsoft Outlook Versions Are Affected?
Microsoft’s published CVE record identifies affected Microsoft 365 and Office LTSC products.
| Product | Published Affected-Version Information |
|---|---|
| Microsoft 365 Apps for Enterprise | Affected builds are determined by Microsoft’s Office security release and servicing-channel information. |
| Microsoft Office LTSC 2021 | Versions below 16.0.14334.21048 in the published affected range. |
| Microsoft Office LTSC 2024 | Versions below 16.0.17932.21140 in the published affected range. |
The affected products include 32-bit and 64-bit installations as identified in the vulnerability record.
Important: The table is not a complete inventory of every Outlook product or deployment configuration. Use Microsoft’s advisory to determine whether your particular edition, build and update channel are affected.
Do not assume that Outlook on the web, the new Outlook application, classic Outlook for Windows and Outlook for Mac have identical vulnerability exposure merely because they share the Outlook name.
How to Fix CVE-2026-124194 in Microsoft Outlook
The primary remedy is to install the appropriate Microsoft security update.
Microsoft provides instructions for updating Microsoft 365 and Office applications on Windows.
Method 1: Update Microsoft 365 or Outlook
- Save your work and close any unnecessary Office documents.
- Open Microsoft Outlook or another installed Microsoft 365 desktop application.
- Select File.
- Choose Office Account or Account, depending on the application.
- Find the Product Information section.
- Select Update Options.
- Click Update Now.
- Allow Microsoft 365 to check for and install available updates.
- Restart Office applications if prompted.
- Confirm the installed build against Microsoft’s security advisory.
If the Update Now option is unavailable, the installation may be managed by your organisation.
In that situation, contact your IT administrator rather than attempting to bypass corporate update policies.
Official instructions: Microsoft Support — Update Microsoft 365 or Office for Windows.
Method 2: Check Your Outlook Version and Build
Before and after installing updates, check the version information displayed by Office.
- Open classic Outlook for Windows.
- Click File.
- Select Office Account.
- Look under Product Information.
- Open About Outlook if you need the complete build number.
- Record the product name, version and build.
Compare the results with Microsoft’s CVE-2026-124194 security update table.
Microsoft 365 installations use different servicing channels. Two computers can be fully updated according to their assigned channels while showing different build numbers.
Therefore, avoid comparing your version with a random screenshot from another computer.
Method 3: Protect Yourself From Suspicious Message Files
Even after patching, safe handling of email attachments remains important.
Attackers frequently use business-related subjects to persuade recipients to open unexpected files.
Examples of suspicious messages include:
- Unexpected invoices or payment confirmations.
- Urgent payroll correction notices.
- Unrequested delivery or shipping documents.
- Fake Microsoft 365 account warnings.
- Messages claiming to contain confidential legal documents.
- Unsolicited meeting invitations containing unusual attachments.
Be particularly cautious with unexpected Outlook message files, including files with the .msg extension.
A familiar sender name is not sufficient proof that a file is safe. Email accounts can be compromised, and sender information can be spoofed.
When a message is unexpected, verify it through a separate trusted communication channel before opening the attachment.
Method 4: Strengthen Microsoft 365 Account Security
Installing the patch addresses the specific vulnerability, but organisations should also review their broader identity-security controls.
Enable Multifactor Authentication
Multifactor authentication adds an additional verification step when users sign in.
It can reduce the risk of some credential-based attacks, although it does not guarantee protection against every NTLM-related attack or authentication relay scenario.
Review Legacy Authentication
IT administrators should assess where NTLM remains in use and whether it can be restricted safely.
Changes to authentication policies should be tested because older applications and network resources may still depend on legacy protocols.
Use Endpoint Protection
Keep Microsoft Defender or another approved endpoint security solution updated.
Organisations can also use endpoint detection and response tools to investigate suspicious activity and potential credential exposure.
Apply Least-Privilege Access
Employees should not have administrative privileges or broad network permissions unless their work requires them.
Reducing unnecessary access can limit the damage from a compromised account.
Method 5: Review Outbound Network Authentication
Because this vulnerability can involve connections to attacker-controlled network locations, network configuration is relevant.
Administrators may consider restricting unnecessary outbound SMB traffic, particularly TCP port 445, at appropriate network boundaries.
This can reduce exposure to certain credential-leak scenarios, but it should not be treated as a complete replacement for installing the Microsoft patch.
Blocking network protocols without evaluating business requirements can interrupt legitimate file sharing and other applications.
Any changes should follow the organisation’s approved security and change-management process.
What Should You Do If You Opened a Suspicious Outlook File?
Recommended response steps include:
- Stop interacting with the suspicious file.
- Do not forward it to colleagues.
- Report the message using your organisation’s approved phishing-reporting process.
- Tell the security team when the file was opened.
- Provide the sender details and message subject without publishing confidential information.
- Allow IT staff to check the device, authentication logs and network activity.
- Install the relevant security update when instructed.
- Follow incident-response guidance if credentials may have been exposed.
Changing your password may be appropriate after a suspected credential incident, but password rotation alone does not replace investigating active sessions, possible relay activity or unauthorised access.
Security teams should determine whether further containment, credential revocation or endpoint isolation is necessary.
How IT Administrators Should Prioritise the Outlook Patch
For businesses managing dozens or thousands of Windows devices, applying updates consistently is more complicated than updating a single computer.
A practical response starts with identifying affected installations.
| Priority | Recommended Action | Reason |
|---|---|---|
| Immediate | Identify affected Outlook and Microsoft 365 installations. | Establish the exposure across managed endpoints. |
| Immediate | Deploy the applicable November 2026 Office security update. | Address the actively exploited vulnerability. |
| High | Review suspicious message-file activity and network authentication events. | Identify potential exploitation attempts. |
| High | Verify update installation and device compliance. | Confirm the fix reached affected systems. |
| Ongoing | Review NTLM usage and outbound authentication controls. | Reduce future credential-exposure risks. |
| Ongoing | Train staff to report suspicious attachments. | Improve detection and reduce risky user interaction. |
IT teams using Microsoft Intune, Configuration Manager or another endpoint management platform should check deployment reporting rather than assuming that issuing an update automatically means every device has installed it.
Devices that are offline, out of support or assigned to unusual servicing channels may require separate attention.
Is CVE-2026-124194 a Critical Vulnerability?
Microsoft classifies CVE-2026-124194 as Moderate, with a CVSS score of 6.5.
That classification reflects the vulnerability’s technical characteristics, including its requirement for user interaction.
However, the flaw has been exploited in real attacks.
This distinction is important because patching decisions should consider both technical severity and actual threat activity.
An actively exploited Moderate-rated vulnerability can deserve more urgent remediation than a Critical-rated vulnerability with no known exploitation, depending on the organisation’s exposure and business context.
CISA’s Known Exploited Vulnerabilities catalog helps security teams identify flaws that have demonstrated real-world exploitation.
CISA Adds CVE-2026-124194 to Known Exploited Vulnerabilities
CISA added the Outlook vulnerability to its Known Exploited Vulnerabilities catalog on November 10, 2026.
The catalog identifies vulnerabilities with evidence of active exploitation.
The listing includes a remediation due date of November 24, 2026, under the applicable federal directive framework.
That date is relevant to covered US federal agencies and their specific compliance requirements. It is not a general permission for every organisation to delay patching until November 24.
Businesses and individual users should follow Microsoft’s remediation guidance and their own risk-based patching policies.
Official reference: CISA Known Exploited Vulnerabilities Catalog.
Does CVE-2026-124194 Affect Outlook on the Web?
The published affected-product information identifies Microsoft 365 Apps for Enterprise and Office LTSC desktop product families.
It does not establish that every service or application carrying the Outlook name is vulnerable.
For example, Outlook on the web runs through a browser, while classic Outlook for Windows is a locally installed desktop application.
These products can have different security architectures and update mechanisms.
Users should rely on Microsoft’s affected-product table rather than assuming that every Outlook experience has the same exposure.
Does Updating Windows Automatically Fix the Outlook Zero-Day?
Not necessarily.
Windows and Microsoft 365 applications may receive updates through different servicing mechanisms.
Installing a Windows cumulative update does not automatically prove that the relevant Office security update has also been installed.
Administrators should verify both operating-system patch compliance and Office application patch compliance.
For personal computers, open the Microsoft 365 application and check for Office updates using the supported procedure.
Microsoft November 2026 Patch Tuesday: Why It Matters
The Outlook zero-day is part of a much larger November 2026 security release.
Security researchers and technology publications have reported more than one thousand vulnerabilities addressed across Microsoft’s products and components during this release cycle.
Published totals differ depending on whether researchers include Microsoft Edge and other separately counted vulnerabilities.
For example, some reports count approximately 1,093 newly released vulnerabilities in their core Microsoft tally, while broader counts exceed 1,200.
Rather than relying on one headline total, administrators should review the products actually deployed in their environments and the applicable vendor advisories.
The most urgent practical lesson is that organisations need a reliable process for identifying actively exploited vulnerabilities and verifying that security updates have been applied.
How to Verify That Your Outlook Update Was Successful
After installing the relevant update, complete these checks:
- Restart Outlook and other Office applications if required.
- Open File → Office Account.
- Review the version and build information.
- Compare the build with Microsoft’s security release information.
- Confirm that no additional Office updates are pending.
- For managed computers, verify the device’s compliance status with IT.
If Outlook continues to show an old build after updating, the device may be using a managed update channel or may have encountered an installation problem.
Contact Microsoft Support or your organisation’s help desk for the appropriate next step.
Frequently Asked Questions
What is CVE-2026-124194?
It is a Microsoft Outlook spoofing vulnerability that can expose Windows authentication information when a user opens a specially crafted message file in an affected Outlook application.
Is the Outlook zero-day actively exploited?
Yes. Microsoft’s vulnerability information identifies exploitation, and CISA added CVE-2026-124194 to its Known Exploited Vulnerabilities catalog on November 10, 2026.
When was CVE-2026-124194 fixed?
Microsoft published the security fix on November 10, 2026, as part of its November security update release.
What is the CVSS score?
The published CVSS v3.1 base score is 6.5, corresponding to Medium severity. Microsoft labels the issue Moderate.
Can attackers steal my Outlook password?
The vulnerability can expose NTLM authentication information. This is not identical to Outlook displaying a plaintext password, but the exposed material may be useful in credential attacks.
Does the vulnerability require clicking an attachment?
The described exploitation scenario requires a user to open a specially crafted message file. Simply receiving an ordinary email does not establish successful exploitation.
How do I install the Outlook security update?
For supported Microsoft 365 installations, open an Office application, select File, then Account or Office Account, choose Update Options and click Update Now. Managed devices may require administrator deployment.
Does Windows Update fix CVE-2026-124194?
Do not assume that installing a Windows cumulative update also installs the relevant Office patch. Verify the Office application update separately.
Is Outlook for Mac affected?
The published affected-product information reviewed here identifies specific Microsoft 365 and Office LTSC product families. Check Microsoft’s current advisory for product-specific applicability rather than assuming all Outlook editions are affected.
Is Outlook on the web vulnerable?
The affected-product information does not establish that Outlook on the web is affected in the same way as the listed desktop products. Consult Microsoft’s advisory for the current scope.
Should businesses disable NTLM?
Organisations should review unnecessary NTLM usage and consider appropriate restrictions. Changes should be tested because some legacy systems may depend on NTLM authentication.
What if I opened a suspicious Outlook file?
Report the incident to your IT or security team, preserve relevant details and follow the organisation’s investigation and remediation instructions.
What is the CISA remediation deadline?
The KEV entry lists November 24, 2026, under the applicable federal remediation framework. Other organisations should patch according to their own risk and vendor guidance, preferably without unnecessary delay.
Official Sources and References
- Microsoft Security Response Center — CVE-2026-124194
- CISA — Known Exploited Vulnerabilities Catalog
- NIST National Vulnerability Database — CVE-2026-124194
- Microsoft Learn — Office Update History
- Microsoft Support — How to Update Office
Related Cybersecurity and Technology Guides
For computer troubleshooting and technical explainers, explore 1000 Science Fair Projects — Tech.
TL;DR: Outlook Zero-Day CVE-2026-124194
- Vulnerability: Microsoft Outlook spoofing flaw.
- CVE: CVE-2026-124194.
- Severity: Moderate, CVSS 6.5.
- Exploitation: Confirmed.
- Patch date: November 10, 2026.
- Risk: Exposure of Windows NTLM authentication information.
- Attack requirement: User opens a specially crafted message file.
- Fix: Install the appropriate Microsoft 365 or Office security update.
- Additional protection: Avoid suspicious attachments, review NTLM exposure and monitor authentication activity.
Bottom line: Update affected Outlook installations promptly. The vulnerability’s Moderate severity rating should not obscure the fact that attackers have already exploited it.
Editorial note: Published November 11, 2026. This independent security guide is based on Microsoft’s CVE advisory, CISA vulnerability information and Microsoft support documentation. Product applicability, build numbers and remediation instructions may change. This website is not affiliated with Microsoft or CISA.